Validation Summit 2026 On Demand | Picus Security
Validation Summit 26' · Now on demand
Get a demo
Now on demand

Picus presents · Digital summit · Recorded October 2026

The Validation
Summit 26'

Attackers run on machine time.
Your validation runs on a calendar.

The blueprint for readiness when attackers have AI. Four sessions from people with no reason to agree with each other: what changed, what to do about it, and how enterprises are already proving it works.

Sessions4 recordings
RuntimeAbout 2h 15m
HostRon Eddings
FormatWatch anytime
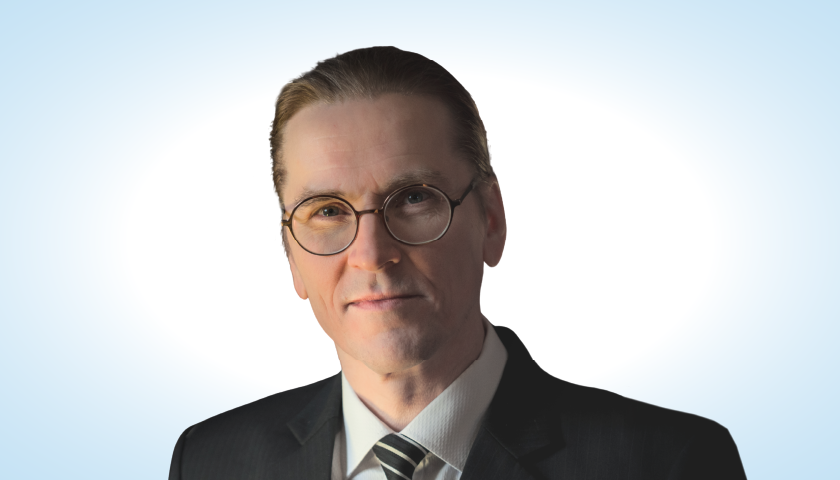
Mikko HyppönenKeynote
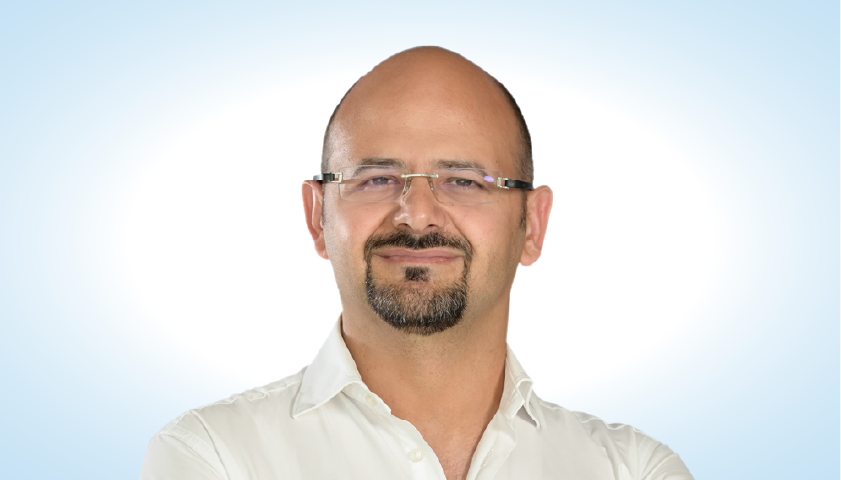
Volkan ErturkPicus
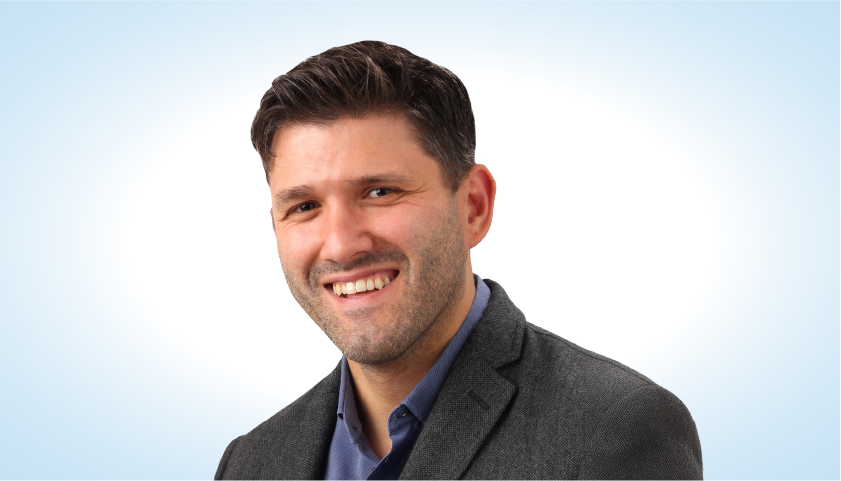
Korhan AcarPicus
Ceylin YavuzPicus
Gürsel ArıcıPicus
Tomás MaldonadoNFL
David B. CrossAtlassian
Alexandria San MiguelLuxury retail
Ron EddingsHost
Detail A · 4 sessions · approx. 2h 15m

Detail A · The sessions

Four sessions.
One blueprint.

Watch them in order, or start with the one your board keeps asking about. Every session is recorded in full, with chapters on YouTube so you can jump straight to the part you need.

Part 01 · Opening keynote

Runtime · 24 mins

Mikko Hyppönen Keynote: Three Decades in Security. This One Is Different.

Mikko Hyppönen, malware researcher since 1991

From the ILOVEYOU worm to AI-discovered zero-days: why this shift is unlike any before it, and why AI-enabled attacks need AI-enabled defense.

What you will learn

  • 01Why ransomware hunts exploitable bugs, not companies
  • 02How frontier AI is changing zero-day discovery
  • 03Why continuous testing is now essential
View 01 · RecordingWatch now

Part 02 · The answer

Runtime · 52 mins · includes Q&A

Adaptive Validation: Security Testing in the AI Era

Volkan Erturk, Co-founder and CTO, Picus Security

Exploitation now takes hours, so calendar testing leaves gaps. Volkan introduces Adaptive Validation: testing triggered by new threats, CVEs and changes in your environment.

What you will learn

  • 01How BAS, autonomous pentesting and exposure validation fit together
  • 02From threat signal to action in under six hours with Numi AI
  • 03A practical adoption roadmap, plus live Q&A
View 02 · RecordingWatch now

Part 03 · The demo

Runtime · 23 mins

See It Run: One CVE From Exposed to Closed

Korhan Acar, Ceylin Yavuz and Gürsel Arıcı, Picus Security

One critical CVE, three validation methods, one evidence-based answer, walked live from three team seats.

  • BlueBreach and Attack Simulation. Which controls block and detect the threat.
  • RedAutonomous Penetration Testing. The attack path from SharePoint toward Domain Admin.
  • GreenExposure Validation. Which assets to patch first, on evidence.
View 03 · RecordingWatch now

Part 04 · CISO fireside

Runtime · 37 mins

Hear It From the CISOs: Preparing for Mythos-Class AI Attacks

CISOs from the NFL and Atlassian, and a luxury retail security lead

Three security leaders on how they are adapting to Mythos-class attacks: what to prioritize, and how to prove defenses work.

What you will learn

  • 01Why CVSS alone cannot set priorities
  • 02Moving from periodic pentests to continuous validation
  • 03Using risk indicators and AI agents to respond faster
View 04 · RecordingWatch now
Detail B · Your environment

Get a demo · End of drawing

See what this looks like in your environment

The summit covered how AI adversaries operate at machine speed, why controls need to be proven rather than assumed, and what the path from manual to autonomous validation looks like. If you are wondering how it applies to your stack, your gaps and your priorities, this is the next step.

  • 01Where your defenses hold, and where they miss.
  • 02Which attack paths to your critical assets are real.
  • 03What closing the gaps looks like in practice.

Talk to our team · 30 mins · no slides required

Request a demoPicus Security

Loading the form...